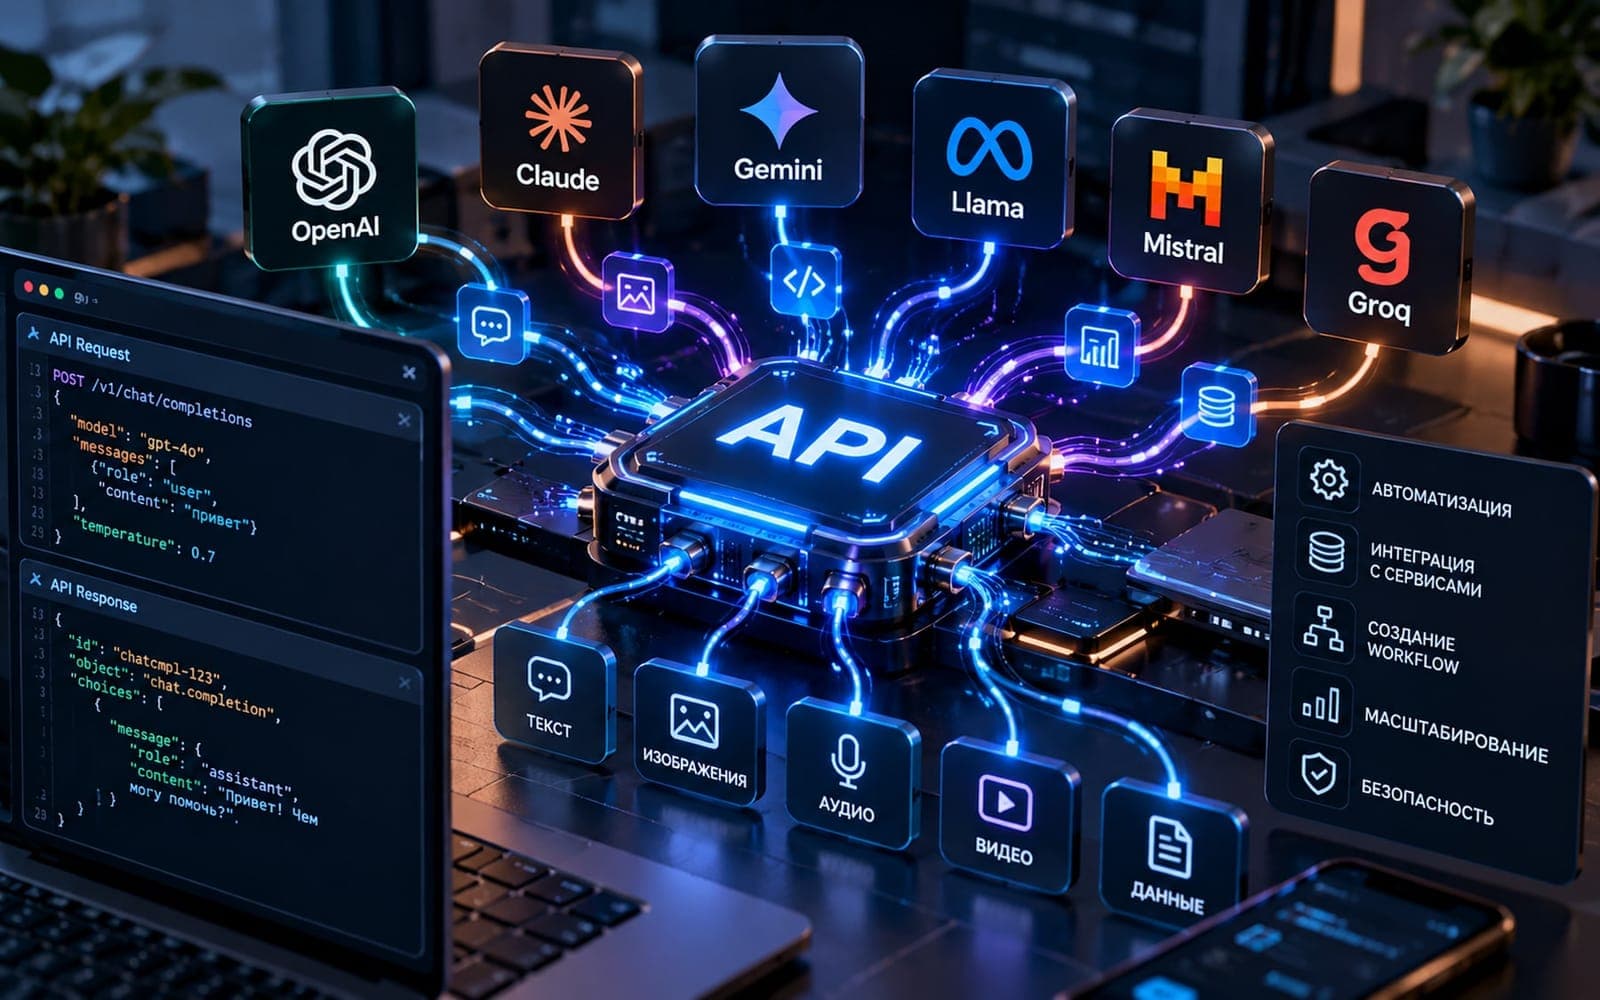
An API is a defined way for one piece of software to request data or an action from another. It is what lets a website create a CRM lead, a payment service report a result or a mobile app read an account balance. A useful API is not merely a collection of URLs: it is a contract about data, permissions, errors and change.
Design around real actions
Start with the business events and records the integration needs. Name operations clearly and return only the data a client requires. Describe accepted input, possible responses and error conditions. Documentation and examples should match the deployed behaviour, not an idealised version from an early specification.
Security is part of the contract
Authenticate callers and authorise each operation for the specific record, not only for the general role of the user. Limit request rates and validate all incoming data. Keep secret tokens on trusted servers. Audit operations that change money, permissions or customer information.
Expect unreliable networks
Requests can time out after the other service has already completed the work. Design important writes to be idempotent, so a retry does not create duplicate orders or charges. Add timeouts and clear retry rules. For event-driven integrations, log delivery attempts and provide a way to replay failed events.
Plan for change
Clients and services rarely update at exactly the same moment. Introduce compatible changes where possible, version breaking changes deliberately and monitor which clients still use old behaviour. A well-kept API lets the product evolve without turning every integration into a fragile custom patch.